
From detection to investigation
The session examines EDR blind spots around fileless attacks, zero-days and AI-driven evasion, how an incident develops between a missed signal and response, and analysts validating threats instead of chasing alerts.
Containment-first SOC
The Post-EDR model keeps unknown activity in an isolated environment while it is analyzed. The program includes attack scenarios, signal validation, strategy-focused SOC work, and effects on dwell time and alert fatigue.
Speakers and moderator
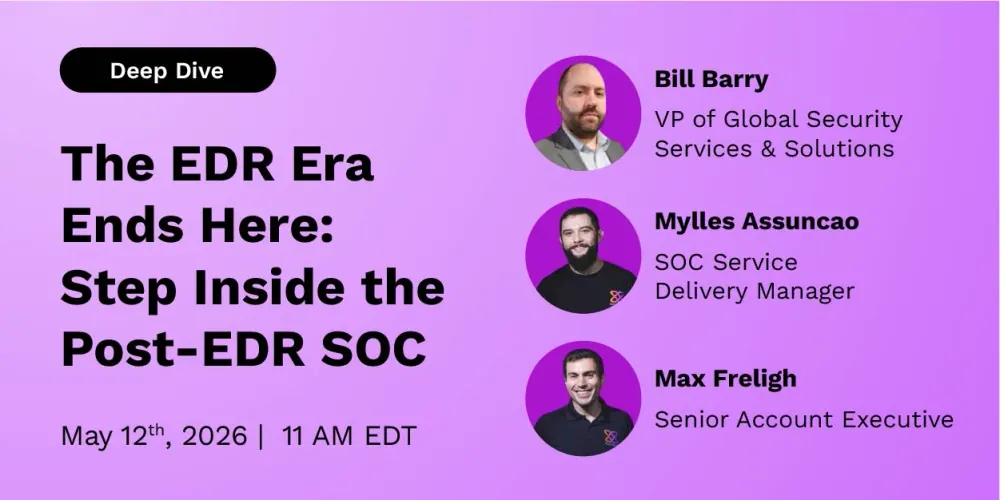
- Bill BarryVP of Global Security Services & Solutions
- Mylles AssuncaoSOC Service Delivery Manager
- Max FrelighSenior Account Executive · moderator