
Customer case
K–8 district consolidates IT management to support secure remote learning
A district serving more than 5,800 students across nine schools coordinated computer management and IT support during the shift to remote instruction.
XCITIUM / Knowledge library
Customer experiences, practical security guides and technical research. Find what you need by topic and material type.
195 materials
Customer case
A district serving more than 5,800 students across nine schools coordinated computer management and IT support during the shift to remote instruction.
Customer case
A manufacturer with field staff sought simpler device management and protection for project and business records.
Customer case
A state technology-services agency established central policy and delegated administration across more than 25,000 Windows, Linux and Mac endpoints.
Customer case
The 16-site FQHC sought remote support; five information-security staff managed its Xcitium Advanced and Endpoint Manager deployments.

Guide and research
Evaluate endpoint protection against your environment: compatibility, unknown programs, management and pilot testing.

Guide and research
The role of static and behavioural analysis, application control and EDR in detecting and investigating endpoint threats.

Guide and research
Systematically design, test and maintain detection rules using a threat model and available telemetry.
Guide and research
Identify unauthorized data transfers through email, cloud services and removable media, and prepare a coordinated response.
White paper
Xcitium presents this paper for security leaders and teams assessing how to govern unknown code, document oversight and demonstrate that cyber controls are being enforced.
White paper
Xcitium discusses sandbox delays, kernel-level isolation for unknown files and ways to maintain user workflows during analysis.
White paper
Xcitium presents this paper around the shift from detection dashboards to runtime enforcement evidence, the principles behind execution governance and reporting for auditors, insurers and boards.
White paper
Xcitium presents a layered model that combines signature databases, behavioral monitoring and kernel-level isolation for unknown files.
Customer case
Amadeus and Xcitium MSP partner Microdium combined ITSM and security for managing thousands of airport kiosks and computer systems.
Customer case
Evergreen Life Services, which supports people with disabilities, sought a simpler and more unified security approach to replace disconnected IT tools.
Customer case
Family-owned Gem State Paper & Supply sought EDR after an encryption incident and began monitoring its devices through the Xcitium portal.

Customer case
An unnamed Minnesota company producing malt and brewing supplies faced recurring weekly infections and a fragmented security stack.
Customer case
A nonprofit health centre in Ontario began with remote support tools and moved to Xcitium Advanced; it had more than 112 endpoints.
Customer case
An unnamed hospital evaluated alternatives to Kaspersky, and a ransomware demonstration influenced its choice of approach.
Customer case
An unnamed MSP founder described MDR costs and revenue across 9,000 endpoints; Xcitium used this historical account in an illustrative company valuation model.
Customer case
Two IT staff selected protection for more than 350 endpoints and 30 servers across 14 locations holding financial and personal records.
Customer case
An evangelistic nonprofit serving the motorcycling community replaced disparate antivirus tools with a central console to protect membership and donation records.
Customer case
A community school district adopted Xcitium Advanced and central management to address malware exposure on devices used by students for email and web access.
Customer case
The media-industry association evaluated EDR, XDR, log analysis and provider support in one solution for roughly 150 endpoints.
Guide and research
BEC attacks exploit business trust to redirect payments, change payroll details and obtain sensitive data. Learn the common patterns and combine technical controls with financial verification.

Guide and research
An EDR agent observes files, processes and network activity on endpoints to surface suspicious behavior. Understand how it differs from antivirus, what response actions it can support and what to assess before deployment.
Guide and research
Learn how Xcitium’s risk services program organizes participants, scope and deliverables for gap assessments, vulnerability assessments, penetration tests and awareness services.
Guide and research
Zero Trust does not treat network location as proof of trust. Rechecking identity, device posture and context for access requests helps limit permissions and constrain lateral movement.
Guide and research
How to prepare a phishing exercise, assess staff responses and use the results to improve learning and work procedures.
Guide and research
Attackers may impersonate an executive, supplier, IT colleague or familiar service. Assess requests from email, text, QR codes and social platforms against their context and your organization’s normal approval process.
Guide and research
How to inventory and update remote devices, limit access and prepare for phishing response. The role of EDR in monitoring activity and investigating incidents.
Guide and research
Social engineering persuades a person to disclose information, transfer money or take an unsafe action. Learn how attacks are prepared, which techniques are common and where endpoint tools can help.
Guide and research
Phishing uses email, messages and fake websites to exploit trust and obtain information, account access or money. Learn the main attack types and combine technical controls with operational procedures.
Guide and research
A phishing message may look urgent and convincing while its sender, link or request does not fit the work context. This guide covers what to check before acting and what to do after an incident.
Guide and research
Security in AWS extends beyond choosing a service. It requires clear ownership and ongoing checks for accounts, permissions, data, workloads and monitoring.
Guide and research
Cloud architecture should connect network, identity, application and data controls to the service owner’s actual responsibilities.
Guide and research
An assessment reviews accounts, identity, data, workloads and recovery against risk, then assigns owners and deadlines to remediation.
Guide and research
When selecting EDR, verify actual coverage and response capabilities for cloud-connected devices, virtual machines and managed workloads.
Guide and research
Cloud security combines ongoing governance and technical controls to protect data, applications and infrastructure across customer and provider responsibilities.
Guide and research
A Cloud Workload Protection Platform is a category of workload-level visibility and controls; verify actual coverage by asset type, runtime and responsibility boundary.
Guide and research
In hybrid environments, risks arise as resources, identities and data cross multiple networks and management domains; map ownership and traffic flows.
Guide and research
Reduce risk across multiple cloud providers with a common inventory and policy goals, while validating configuration and ownership for each service.

Guide and research
Changing a DNS server changes how domain names are resolved to IP addresses. The setting can live on a device or on the router. Record the current configuration first, then review the new resolver’s privacy, filtering and availability policies.
Guide and research
A gateway is a point that passes traffic between networks or protocols. Understanding its role and where router, switch and firewall functions begin helps teams design and protect a network.

Guide and research
A site may fail to load because of a filter, DNS error, browser issue, regional restriction or service outage. Identify the cause first and choose a lawful fix that follows workplace or school network rules.
Guide and research
A cloud-managed endpoint tool can centralize policy and visibility, while coverage, agent behavior and response vary by product. Evaluate it against real devices and operating needs.
Guide and research
A VPN can connect a remote user to a private network and route traffic through organizational controls. Access should be governed alongside device health, identity and authorization.
Guide and research
A firewall applies connection policy by IP address, port and protocol; application and connection-state inspection depend on its capabilities. EDR helps investigate process and file activity on endpoints. Some suites include a host firewall, which does not automatically replace network-boundary control.
Guide and research
An IDS looks for suspicious activity in network or host signals; EDR centers on endpoint telemetry and response. Their visibility and intervention options depend on the implementation.
Guide and research
A DDoS attack attempts to disrupt service availability by sending a flood of traffic or requests from many sources. Preparation spans capacity, network providers, application behavior and incident response.
Guide and research
Small business network security goes beyond choosing a firewall: consider devices, email, remote access, cloud accounts, backups and monitoring. Select a provider against verifiable needs and service terms.
Guide and research
A WAF can evaluate HTTP and HTTPS requests against application rules before they reach a web application. It does not replace secure coding, authentication or server patching.
Guide and research
An allowlist permits only preapproved IP addresses, domains, email addresses or applications. Lists complement firewall and identity policies; they do not replace them.
Guide and research
An IDS looks for intrusion indicators in selected network or host signals. A SIEM collects and correlates events from multiple systems; the categories complement each other.
Guide and research
Active Directory governs accounts, groups and computers, so its security depends on identity controls, privileged administration, domain controllers and recovery working together.
Guide and research
Public resources and excessive permissions can emerge in complex, changing AWS environments. Effective control needs an inventory, an owner, clear rules and verified remediation.
Guide and research
EDR helps investigate suspicious endpoint behavior, but it does not determine account ownership or required access. Defense should connect identity and device signals.
Guide and research
IAM governs identity creation, authentication, permissions and revocation. A sound program connects these steps to hiring, role changes, contractor access and departures.
Guide and research
Digital identity connects employees, administrators, applications and service accounts to systems. Identity security governs their permissions, authentication and activity monitoring.
Guide and research
AD FS can provide federated authentication between on-premises Active Directory and trusted applications. Security depends on server hardening, trust configuration and application dependency management.
Guide and research
Multifactor authentication reduces password-theft risk, but methods differ in phishing resistance and implementation quality. Match coverage and recovery to account risk.
Guide and research
PAM governs high-impact access for administrators, services and emergency accounts. An effective program combines policy, process and technical controls to reduce standing privilege.
Guide and research
Zero Trust does not treat network location or ownership as proof of trust. The architecture connects identity, device and resource decisions for each access request.
Guide and research
Zero Trust is an approach to protecting resource access across remote work, cloud and shared infrastructure. Adoption requires staged changes shaped by organizational risk and architecture.
Guide and research
A managed identity service can support an internal team with account and access operations. Customer and provider responsibilities, data access and escalation must be agreed in advance.
Guide and research
Identity management governs how users, devices and services access organizational resources. As remote work and cloud applications grow, consistent ownership, role assignment and deprovisioning matter.
Guide and research
Decrypting a drive removes a layer that protects data from someone with physical access to a lost or stolen device. Check the reason, recovery key and device policy first.
Guide and research
A remote-work security stack should connect endpoint response, application access, DLP, identity, backup and file sharing into one operating process.
Guide and research
Encryption turns readable data into a form that cannot be understood without a key. Apply it to the places where data is stored, transmitted and used.
Guide and research
When data spans SaaS, storage and backups, organizations need to find it, govern access and verify recovery.
Guide and research
DLP helps organizations see how sensitive data moves across endpoints, network traffic and cloud services, then respond to policy violations.
Guide and research
For cloud-managed employee endpoints, verify OS and agent coverage, telemetry, patching and response ownership.
Guide and research
Endpoint DLP can monitor sensitive-data use and transfer on supported managed endpoints; verify coverage by OS, application and action.
Guide and research
Identity-based segmentation limits access to specific resources according to user, role, device and service identity.
Guide and research
Cloud encryption protects stored and transmitted data; the right approach depends on the service model, key control and recovery ownership.
Guide and research
Network, endpoint and cloud DLP can observe different data states; actual coverage depends on channels and integrations.
Guide and research
A vulnerability management program makes discovery, prioritization, remediation and verification a repeatable process with accountable owners. Define its scope, decision rights and completion criteria.
Guide and research
A zero-day attack exploits a previously unknown flaw. Distinguish the vulnerability, disclosure, fix availability and evidence of exploitation, and plan investigation of suspicious activity.
Guide and research
Define a managed security service’s contracted scope, decision rights and handoffs. Connect monitoring, investigation and remediation to verifiable evidence and clear responsibility.
Guide and research
Do not rank findings by technical score alone. Combine exploitation evidence, actual reachability and business impact to set a priority an accountable owner can act on.
Guide and research
Connect a security signal to an analyst, an authorized decision and a verifiable action. Coordinate the distinct jobs of testing, incident response and monitoring tools through a shared workflow.
Guide and research
Distinguish a system weakness, an attack technique and malware. Record code, configuration and identity weaknesses separately from the actions that exploit them.
Guide and research
Operate vulnerability management as a repeatable practice with clear cross-team ownership, reassessment triggers and decision records. Preserve evidence from discovery through outcome verification.
Guide and research
Track an individual finding from assessment through disposition and action to evidence-based closure. Use reassessment and reporting to inform the next cycle’s priorities.
Guide and research
As teams adopt assistants, agents and AI integrations, organizations need a record of what is in use, what data it can reach and who owns the decisions.
Guide and research
A cyber risk program connects assets and threats to business impact, assigns treatment owners and revisits decisions over time.
Guide and research
A scan only creates findings. A program covers assets, validates results, prioritizes with business context, tracks fixes and checks again.
Guide and research
Remote computers, mobile devices and IoT equipment differ in software and update options. A review makes assets, baseline requirements and exceptions visible.
Guide and research
Policies, technical controls and operational evidence must work together to protect endpoint data. Fit requirements to the organization’s actual scope.
Guide and research
A cloud provider’s attestation does not remove an organization’s responsibility for its own data, configurations and operations. Manage requirements, responsibility boundaries and reviewable evidence together.
Guide and research
Cloud governance clarifies who provisions, protects, monitors and retires resources. Connect security, cost and operational goals to accountable owners.
Guide and research
EDR brings signals from remote and office devices together. Useful coverage depends on agent health, disconnected devices and a response process that works across them.
Guide and research
Laptops, servers, phones and IoT devices connect in different ways. Endpoint security needs to join asset inventory, updates, access rules and detection into one operating practice.
Guide and research
An endpoint pilot should test coverage, detection and response operations on your devices and workflows, rather than simply demonstrate product features.
Guide and research
Windows endpoint protection spans operating-system and application updates, host controls and endpoint detection. Check the actual configuration and coverage of each layer.
Guide and research
Ethical hacking tests weaknesses in systems with the owner’s authorization. Written permission, clear scope, impact limits and an actionable report are core parts of the work.
Guide and research
Exploit kits can probe browser and plugin weaknesses to deliver malware. Delayed updates, risky web content and excessive user privileges can increase the impact of that chain.
Guide and research
Internet-facing domains, hosts, cloud services and remote access points change over time. External attack surface management helps find unknown assets, confirm ownership and route findings to remediation.
Guide and research
A penetration test validates the impact of weaknesses through agreed scenarios. Without a clear objective, scope and risk boundary, testing can be incomplete or disruptive.
Guide and research
A list of vulnerabilities does not determine risk priority by itself. Combining asset value, internet exposure and exploitation signals turns threat information into remediation decisions.
Guide and research
A continuous process discovers assets and weaknesses, prioritizes remediation and verifies outcomes. Reassessment catches new assets, changes and recurring problems.
Guide and research
Learn how common malware families differ, how adware reaches devices and which changes deserve attention. Follow practical steps to investigate and clean a suspected infection safely.
Guide and research
Learn how fake apps, phishing links, excessive permissions and account theft can affect a phone. Follow practical steps to review app and privacy settings on Android and iPhone and respond to a suspected incident.
Guide and research
A Trojan may disguise itself as a trusted file or app. A user opening it is a common delivery path, but another malicious component can also start the payload. Learn how it differs from a virus or worm, how an attack unfolds, the major Trojan types, warning signs and response steps.
Guide and research
Map cyber threats by attack method and business impact. Match malware, phishing, service disruption, vulnerabilities, insider risk and cloud/API exposure with practical controls and response plans.
Guide and research
Access records, operational logs and security events answer different questions. Choose the sources, keep records searchable and distinguish general log management from SIEM correlation.
Guide and research
SIEM brings security data together, normalizes it and helps teams investigate relationships among events. Learn how collection, normalization, correlation, alerting and reporting fit together.
Guide and research
SIEM, EDR and XDR cover different data sources and security tasks. Compare endpoint investigation, organization-wide correlation and coordinated response, then assess replacement against your own requirements.

Guide and research
Learn how endpoint telemetry, behavior analysis and investigation tools can expose malicious activity. Evaluate visibility, privacy, response and operational readiness together when comparing EDR capabilities.
Guide and research
Trace ransomware’s evolution from file locking to extortion backed by threats to publish stolen data. Build practical plans for backups, access controls, updates and incident response.
Guide and research
Assess prevention, behavioral detection, hunting, isolation and investigation as separate EDR capabilities. Use practical questions to check detection of early attack signs, offline operation, automated actions and recovery limits.
Guide and research
Distinguish file encryption, device locking and threats to expose stolen data. Learn why malware family, delivery method, criminal business model and extortion tactic describe different things.
White paper
Incident response planning, data flow mapping and endpoint protection for school IT teams.
White paper
Five areas for reducing ransomware risk and preparing for recovery.
Guide and research
Endpoint Detection and Response (EDR) monitors endpoint activity and helps investigate suspicious behavior and respond to incidents. Learn its scope, telemetry, investigation and response capabilities, complementary role with SIEM, and selection criteria.
Guide and research
Run an EDR demo as a test of your own workflow, not as a presentation. Evaluate event visibility, analyst investigation, response authority, device compatibility and operating effort against agreed criteria.
Guide and research
Roll out EDR in stages: confirm the device inventory, set telemetry and privacy boundaries, test operating systems, assign response ownership and introduce automation with control.
Guide and research
A security operations center (SOC) brings together people, processes and technology to monitor, assess and respond to an organization’s security events. Learn its six core functions, business value, analyst responsibilities and incident workflow.
Guide and research
Compare the roles of antivirus, endpoint protection platforms (EPP), EDR and firewalls. Use practical questions to choose an architecture that fits your devices, team and incident readiness.
Guide and research
Compare agent, API, network and cloud-level monitoring. Use practical checks to choose a hybrid design that fits privacy, offline coverage, visibility and device-control needs.
Guide and research
Bring inventory, access, updates, network controls and incident readiness into one operating routine for remote staff, mobile devices, servers and IoT equipment.
Guide and research
Learn how known indicators, behavior analysis, deception traps and analyst-led investigation fit together. Follow a hunt from hypothesis to response, review analytical methods and tool examples, and distinguish a compromise assessment from ongoing hunting.
Guide and research
Learn how an external hunting team can address resource and skills gaps, what work a service may include, and how to define collaboration with an internal SOC.
Guide and research
Understand strategic, tactical, operational and technical intelligence, their audiences and how teams use each level. Apply practical criteria to choose sources, prioritize signals and evaluate a platform.
Guide and research
Compare product and service examples including Xcitium, Heimdal, Bitdefender, Snort, SentinelOne and CrowdStrike. Use practical criteria to evaluate EDR features, service scope and network IDS/IPS capabilities.
Guide and research
Check how endpoint, identity, email, network and cloud signals are correlated and which incident response actions are available. Neutral pilot criteria for Cisco XDR and Palo Alto Cortex XDR.
Guide and research
An incident response plan defines roles, decision authority, escalation, communications and recovery steps in advance. See how current NIST guidance differs from older lifecycle models and how to tailor a plan to your assets, services and risks.
Guide and research
DFIR combines incident response with the preservation and analysis of digital evidence. Learn about artifact types, chain of custody, a six-stage workflow, cloud and IoT constraints, anti-forensics countermeasures and team skills.
Guide and research
MDR adds external security specialists and tools to an organization’s detection, investigation and response work. The service’s value depends on monitoring scope, human analysis, authority, escalation, response actions and follow-up reporting.
Guide and research
Compare static inspection, isolated execution and reverse engineering. Turn file, memory and network evidence into detection and response actions.
Guide and research
IaaS, PaaS and SaaS divide operational work differently. This guide explains infrastructure and deployment models, customer and provider security duties, and the roles of core AWS services.
Guide and research
A VPC provides controls for network segmentation, routing and access rules, but it does not secure resources by itself. Pair network design with cloud app visibility, data policies and suitable CASB capabilities.
Guide and research
Plan a migration from inventory and dependencies through strategy, pilot, staged cutover and rollback. Compare tools and define how to validate security, application behavior and costs after the move.
Guide and research
Routers, IP addresses, subnet masks and DHCP work together to help devices find each other on a local network and reach other networks. This guide connects the core concepts with safe diagnostic steps.
Guide and research
TCP supports reliable delivery of a data stream, ICMP carries diagnostic messages, and IP TTL prevents packets from circulating indefinitely. This guide links those concepts to network topology and simple read-only checks.
Guide and research
Wi‑Fi connects to a local network over radio; LTE and 5G use a mobile operator’s radio and core network; DSL uses a telephone line. Choose based on verified availability at your address and work needs, then secure the router and connected devices.
Guide and research
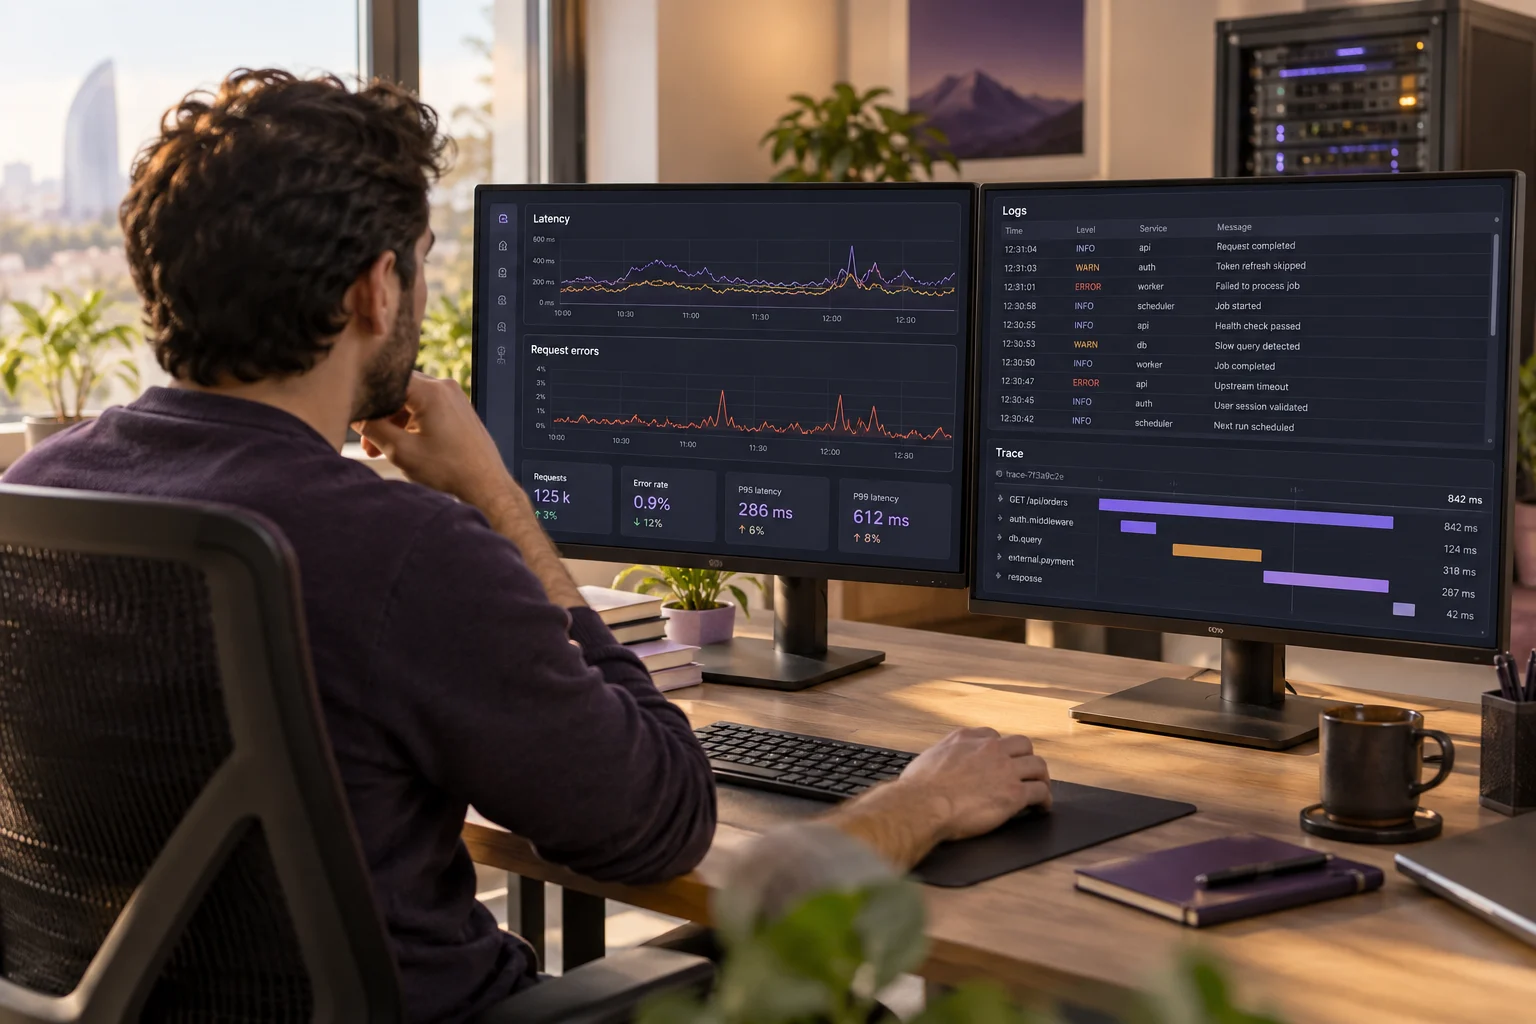
An application log should show more than an error: it should record when it happened, which component was involved, its severity and its outcome. This guide covers event selection, levels, structured formats and sensitive data.
Guide and research
Logs from many servers and applications become searchable when the path from source to archive is planned. This guide covers collection, parsing, normalization, search, alerts, retention and how to evaluate managed logging services.
Guide and research
Event Viewer exposes Windows events, while IIS and other web-server logs record HTTP requests and responses. This guide covers focused filtering, W3C fields, status codes and rotation settings with practical examples.
Guide and research
Monitoring tracks selected indicators; observability connects logs, metrics and traces to help investigate unexpected behavior. This guide explains APM, DevOps feedback, distributed traces and real-user monitoring.
Guide and research
Infrastructure monitoring connects server resources, network paths, cloud services and user-visible outcomes. This guide covers metric selection, SNMP/ICMP/traffic-analysis roles, capacity trends and the responsibility boundary with a cloud provider.
Guide and research
Account attacks range from password guessing to reuse of stolen sign-in pairs. Distinguishing the methods helps teams choose suitable detection and response steps.
Guide and research
NTLM and Kerberos expose different attack paths in Active Directory environments. Defense depends on understanding protocol flows, compromise indicators and recovery actions.
Guide and research
Changing a password with the email provider and refreshing the sign-in saved on a phone are separate actions. Secure the provider account first, then reauthenticate in Apple Mail or another mail app.
Guide and research
Review topology, firewall rules and vulnerability data together to assess real reachability, possible attack paths and the effect of proposed changes.
Guide and research
USB devices and software that move a cursor can interfere with idle locking. Understand the risks and set proportionate rules for accessibility, kiosks and long-running tasks.
Guide and research
Agree on scope, method, evidence and deliverables in advance so the engagement leads to decisions and a remediation plan.
White paper
A Zero Trust plan from data flows to continuous monitoring.
White paper
Why an IT service provider might expand into managed security services.
White paper
Managed detection and response for US state and local government.
Guide and research
Managed IT can cover anything from user support to infrastructure operations. This guide helps define responsibilities, access rules and service measures before an agreement is signed.
Guide and research
SECaaS delivers security technology and operations through a provider. This guide explains how to assess the actual service scope, retained duties and questions to ask before choosing a provider.
Guide and research
Security automation connects repetitive triage, notifications and approved response steps across tools. This guide breaks the work into measurable workflows with checks and human oversight.
Guide and research
Information from people can add context about intent that technical telemetry may not show. This guide explains how to use it in lawful, consent-based and verifiable intelligence work.
Guide and research
Distinguish threat actors by motive and capability, follow how long-running APT activity develops, and build defenses around observed behavior.
Guide and research
Understand malware objectives, bootkit and keylogger mechanisms, botnet structures and how malicious advertising can deliver a threat.
Guide and research
Distinguish misuse of existing tools (LOTL), process manipulation and movement between networked systems. Investigate suspicious Windows and Linux activity using process, account and network evidence.
Guide and research
Make open-source research verifiable, compare honeypots with firewalls, and distinguish the deep web from the dark web.
Guide and research
Recognize how fabricated scenarios and voice calls exploit trust, verify suspicious requests and plan what to do after doxing.
Guide and research
Bring internet-facing assets, cloud resources and unapproved services into the inventory. Tie each finding to an owner, business impact and remediation step.
Guide and research
Coordinate technical investigation, business decisions and communication with affected people through one response plan.
Guide and research
Define the scope, method and reporting for an authorized test, then remediate findings and retest controls.
Guide and research
Bring risk assessment, policies, technical controls and incident response into one management cycle.
Guide and research
Validate behavioral and technical signals without treating them as proof, protect access and investigate with respect for privacy.
Guide and research
Compare changes to critical files against a trusted baseline and validate fixes for legacy software.
Guide and research
Change visible data values for testing and analytics while recognizing that obfuscation does not replace encryption or access controls.
Guide and research
Build ETL/ELT and change-capture flows, compare hybrid and federated analytics, and apply identity and quality controls to each source.
Guide and research
Distinguish 401 from 403, check browser, API and server causes, and monitor repeated failures as a security signal.
Guide and research
Recognize payment deception, phishing, account takeover and fake online stores; protect transfers with independent verification and an incident response process.
Guide and research
Check TPM 2.0 and Secure Boot on a Windows device, enter firmware settings carefully, and prepare the recovery key for an encrypted drive first.
Guide and research
Replace standing administrator rights with access scoped to a task, resource and time window; define request, approval, expiry and audit steps.
Guide and research
Protect data, accounts, endpoints and integrations throughout remote care, from video consultations and patient portals to monitoring devices.
Guide and research
Reduce formula-injection risk when user data enters a CSV, inspect files before import, and protect sensitive exports.
Guide and research
Choose the right steps to recover Windows after a fault or suspicious activity, back up data, and prepare a device for a new owner.
Guide and research
Review a customer-data CRM across roles, exports, connected apps and partner accounts.
Guide and research
Coordinate IT/OT inventory, network boundaries, vendor remote access and continuity planning in connected operations.
Guide and research
An algorithm, a trained model and a model architecture are different things. This guide explains the distinction through prediction, language and security examples.
Guide and research
Text processing, word normalization and LLM response generation are different stages. Learn what each does and where security boundaries matter.
Guide and research
Use business and security examples to distinguish analytics questions, predictions, relationships, bias and statistical variation.
Guide and research
Distinguish raw data storage from prepared reporting. Understand the roles of a data lake, warehouse and BI workflow security controls.
Guide and research
Course completion does not show how employees will respond to a real request. Build a continuing programme around role-specific lessons, phishing practice, a clear reporting route and behaviour measures.
Guide and research
Employees may bring tools into daily work before procurement is involved. Discover current use, define data and permission boundaries, create a fast approval path and choose a narrow pilot with a measurable outcome.
Guide and research
Place an AI agent in an existing support channel: it answers routine questions from approved material and passes unresolved requests to a queue with the conversation context. Keep identity checks and human control for consequential changes.
Guide and research
FTP, RDP, SNMP and TLS serve different purposes. Learn what they carry, which access paths they create and which settings reduce exposure.
Guide and research
Sensors, cameras, IP phones and personal mobile devices add new capabilities to a network. Practical steps for safer procurement, inventory, segmentation, updates and separating work from personal data.
Guide and research
ARP poisoning, DNS redirection, rogue Wi-Fi and other MITM methods exploit network trust. This guide explains where attacks occur, what to look for and how segmentation limits impact.
Guide and research
Forged senders, compromised accounts, executive impersonation and malicious attachments have different signals. Combine SPF, DKIM, DMARC, email gateway controls and payment verification.
Guide and research
SASE combines networking and cloud security in one architecture; UTM brings several security functions onto one platform. Learn how to evaluate them and prepare for attacks on service availability.
Guide and research
An API endpoint is an address a client uses to access a service resource or operation. Design it together with access rules, permissions, load limits and diagnostic data.
Guide and research
Application security covers design, code, dependencies, configuration and runtime behavior. This guide connects early risk discovery with testing for SQL injection, RCE and configuration mistakes.
Guide and research
CI automates frequent integration and checks; CD automates promotion of a validated artifact through environments. Combine early security checks and versioned policy with protection for the pipeline itself.
Guide and research
Virtual machines and containers isolate resources at different layers. Microservices divide an application into independently released components; the choice depends on performance, compatibility, isolation and operational complexity.
Guide and research
Kubernetes schedules containers across a cluster and manages their desired state. AKS provides a managed control plane; teams still need to understand responsibility for workloads, nodes, identity, networking, data and monitoring configuration.
Guide and research
MDR, MSSP and MXDR proposals do not describe the same service. Separate monitoring, investigation, response and the responsibilities your organization retains.
Guide and research
EDR helps investigate suspicious endpoint activity; DLP controls how sensitive data is used and transferred. Compare their goals, coverage and how they work together.
Guide and research
SecOps brings security, IT operations and development specialists together. A SOC is a monitoring and response team or service, while TDR means threat detection and response. Understand the roles and how work is handed over.
No matching material. Try a different search or filter.
Explore case studies and documentation on Xcitium’s official sites.