
01
Connect sources
Integrate relevant log feeds from firewalls, servers, endpoints, identity providers and cloud APIs.
Stage outcome: Centralized log feeds
Xcitium offering
Unified telemetry visibility and SOC validation. Logs from firewalls, servers, endpoints, identity providers and cloud are normalized, correlated and analyzed for behavior.
Discuss your requirements ↗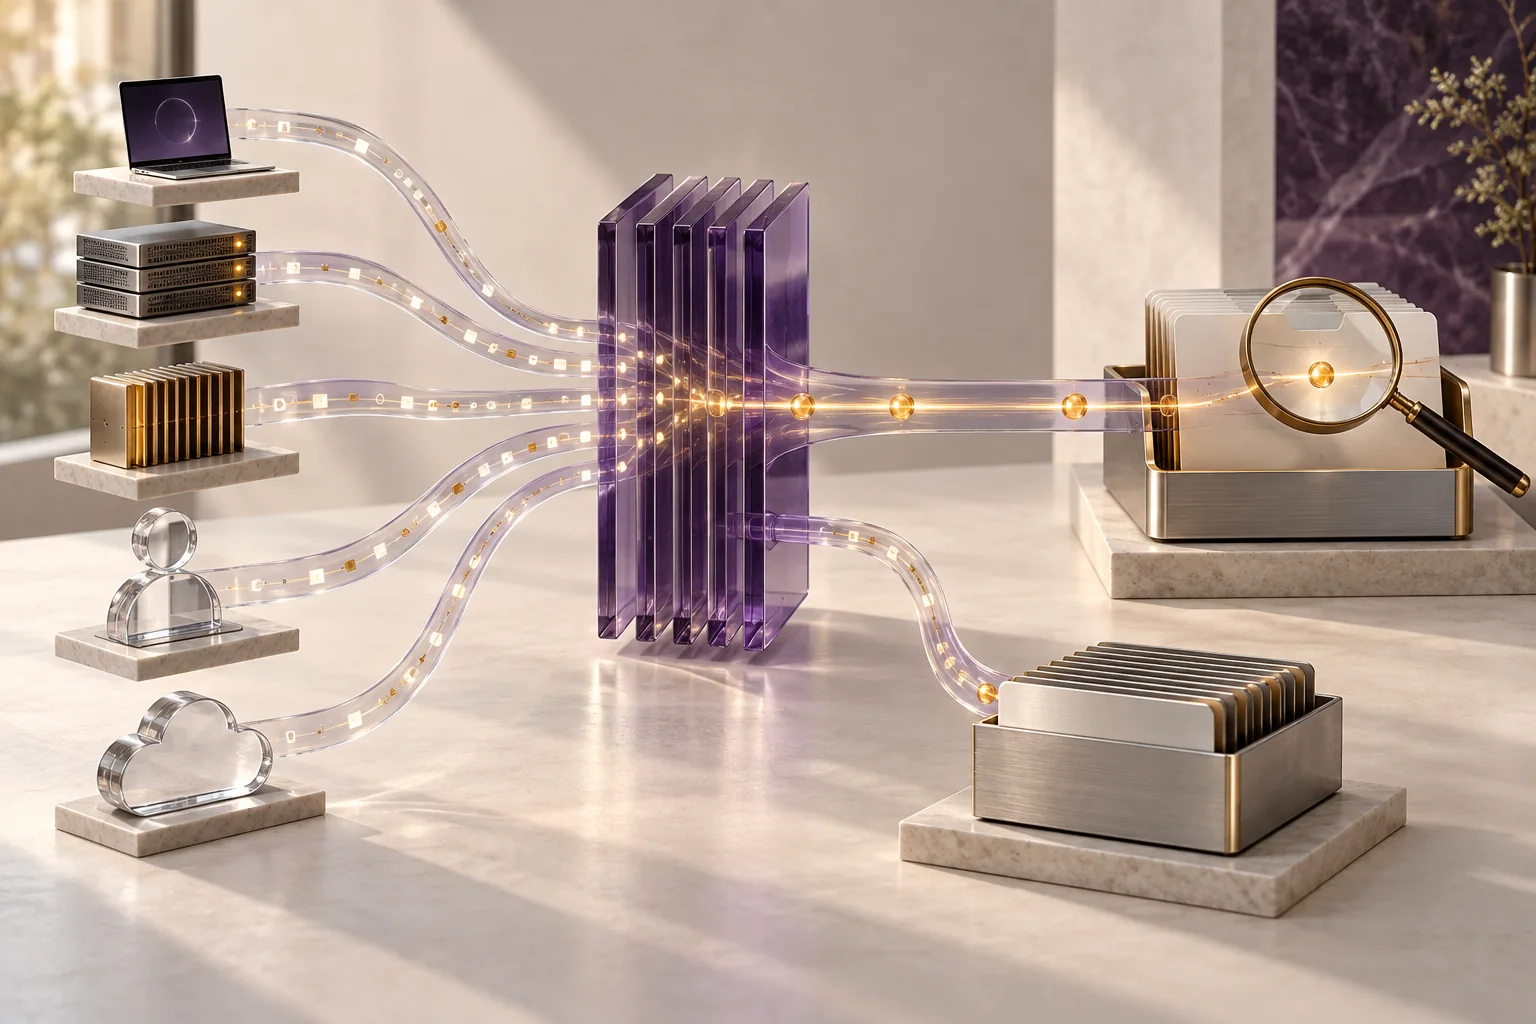
Log sources · SOC validation · documented follow-up
Managed SIEM brings security telemetry from different systems into one workflow. It normalizes and correlates logs, SOC analysts validate alerts and set priorities, then document the result in a ticket with analyst notes and next steps.
Integrate relevant log feeds from firewalls, servers, endpoints, identity providers and cloud APIs.
Stage outcome: Centralized log feeds
The SIEM engine aggregates and enriches telemetry; rules and behavioral analytics surface anomalies across sources.
Stage outcome: Correlated events and behavior signals
SOC analysts validate alerts, assign a risk level and open a ticket for a significant event.
Stage outcome: Prioritized incident ticket
The ticket records analyst notes and next actions. Reporting, audit trails and rule tuning help refine detection over time.
Stage outcome: Notes, next actions and reports
Correlated telemetry, analyst-validated and prioritized events, documented follow-up and reporting evidence that supports audit work.
Capabilities
Centralize, normalize and correlate firewall, server, endpoint, identity and cloud logs for a shared security view.
Onboard sources and normalize formats; correlate events, then have the SOC validate and prioritize alerts.
Hand off tickets with analyst notes and next steps, reports and an audit trail to the response owner.
Log sources, onboarding, retention, rules and response authority are agreed in the proposal.
Compare approaches
| Consideration | Managed SIEM | Managed threat hunting |
|---|---|---|
| Primary focus | Centralize, normalize and correlate firewall, server, endpoint, identity and cloud logs for a shared security view. | Analyst-led, hypothesis-driven threat hunt. |
| Workflow | Onboard sources and normalize formats; correlate events, then have the SOC validate and prioritize alerts. | Hypothesis, search across selected telemetry and deeper finding validation. |
| Output and handoff | Hand off tickets with analyst notes and next steps, reports and an audit trail to the response owner. | Hunt findings, root-cause review and hardening recommendations. |
Before you start
Confirm source inventory, owners, formats, event volume, retention, escalation contacts and who closes the ticket. Trace approved sample events from selected sources through correlation to an analyst ticket; check timestamps, context, priority and recipient.
Which sources and identity/cloud logs are available under current licensing and access?
Who receives a validated alert, and through which channel?
How are retention, reporting and incident-ticket timelines set?
In practice
Events arrive from firewalls, servers, endpoints, identity providers and cloud systems, but analysts lack a joined view. Managed SIEM normalizes and correlates configured logs and adds SOC validation, prioritization and documented follow-up.
What your team gains
Correlated view of configured security telemetry
Validated, prioritized alerts with analyst notes
Tickets and audit-supporting reports
Before you decide
Logs from firewalls, servers, endpoints, identity and cloud can be integrated and correlated.
A SOC analyst validates the alert, prioritizes it and opens a ticket with notes and next steps.
Reports can include analyst notes, audit trails and rule-tuning context; retention and cadence are set by contract.
Next step
Tell us about your environment and priorities to discuss the right solution, pilot scope and rollout in Azerbaijan.