
Managed service · MDR
Managed threat monitoring, investigation and response
Xcitium’s general MDR service combines remote security specialists with 24/7/365 monitoring, proactive hunting, incident response, SIEM, threat intelligence and behavioral analytics.
Discuss your requirements↗
A managed model for monitoring and triage
The service offloads day-to-day security-event triage and analysis to a remote team, with 24/7/365 monitoring and ongoing analysis of endpoint activity and network traffic.
Hunting and actionable notifications
Analysts proactively investigate potential threats; reporting can include high-fidelity notifications about fileless attacks, APT activity and privilege-escalation attempts.
Incident response and remediation steps
MDR provides rapid incident response and remediation steps intended to reduce impact.
Centralized security data through SIEM
SIEM centrally collects, analyzes and correlates security data.
Threat intelligence and behavioral analytics
Global threat intelligence supports detection and prevention, while behavioral analytics looks for unusual activity.
Evaluate MDR step by step
First identify endpoint and network sources, access and retention. Next agree response authority and the approval owner. Trace an approved test event from telemetry to an investigated incident and documented next action before expanding the scope.
Find the right solution
Managed EDR
Managed EDR focuses SOC monitoring and response on endpoint signals.
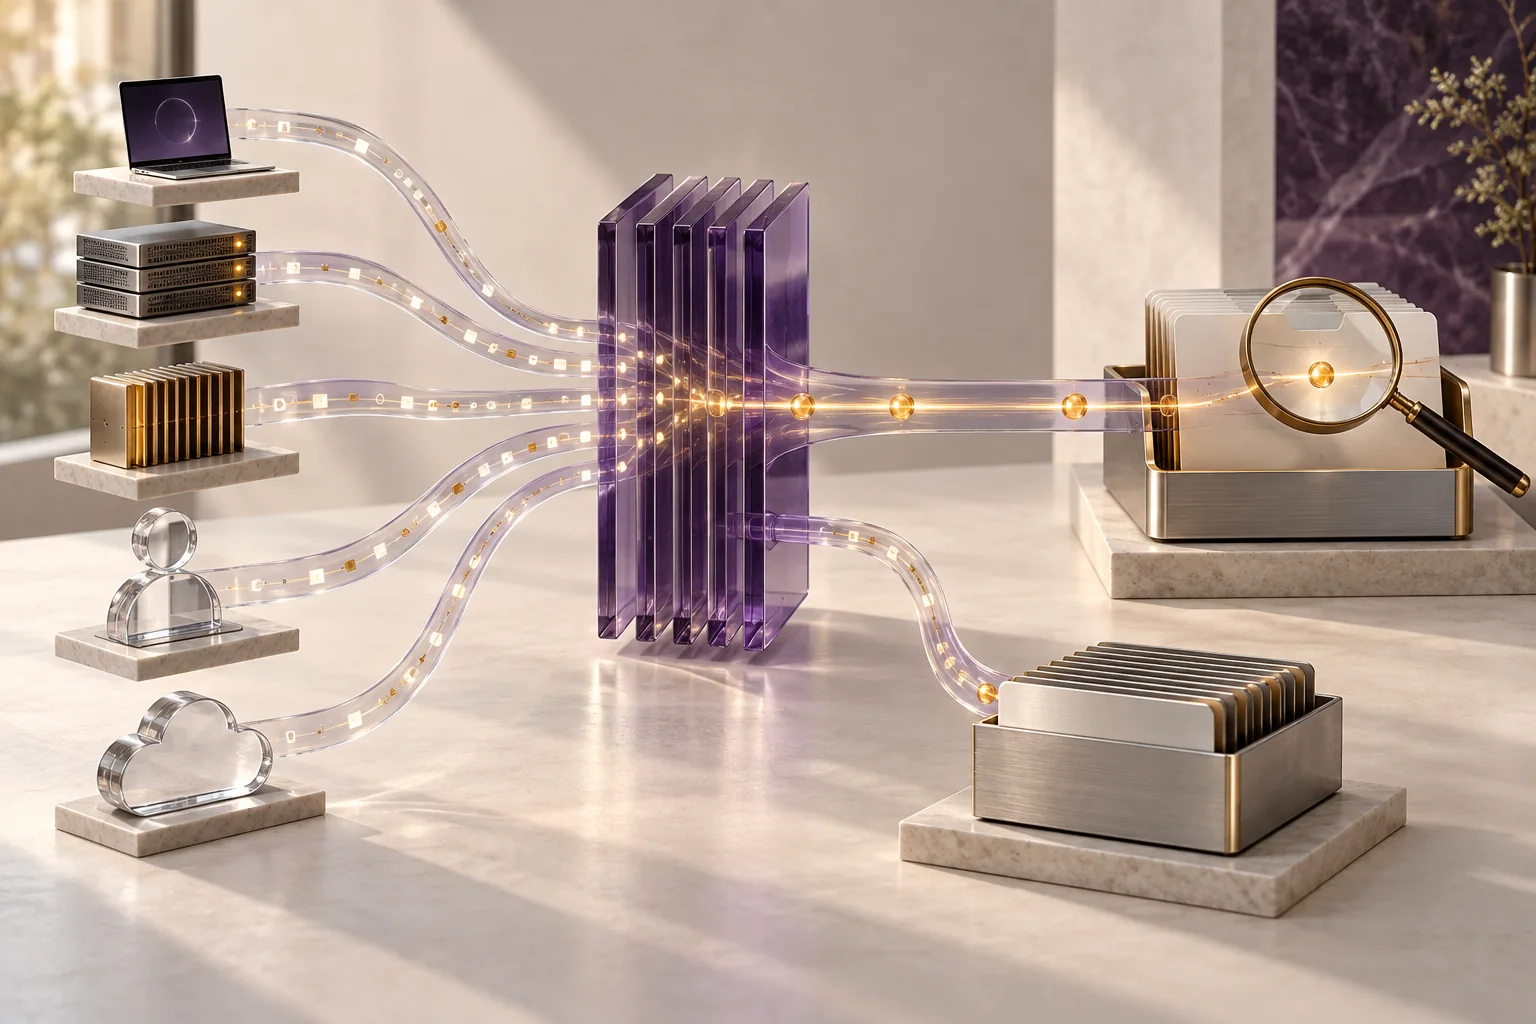
Managed SIEM
Explore SIEM for centralized log collection and correlation.

Managed threat hunting
Review the separate service for proactive analyst-led threat hunting.
XDR
Explore XDR for signal correlation and response workflows.
Questions and answers
Is this MDR different from the Microsoft Defender service?
Yes. General MDR covers endpoint and network activity, hunting, SIEM, threat intelligence and behavioral analytics. The separate Defender service is tailored to Microsoft Defender environments.
What data does MDR monitor?
The service analyzes endpoint activity and network traffic, bringing signals together for investigation.
Xcitium
A plan for your environment
Share your environment, current tools and priorities. Define the scope of the solution and the stages of deployment.