
Xcitium services
Managed SOC services
Bring SOC monitoring, SIEM, threat analysis, and endpoint capabilities together in a managed service for customers.
Discuss your requirements↗
A managed SOC for customer environments
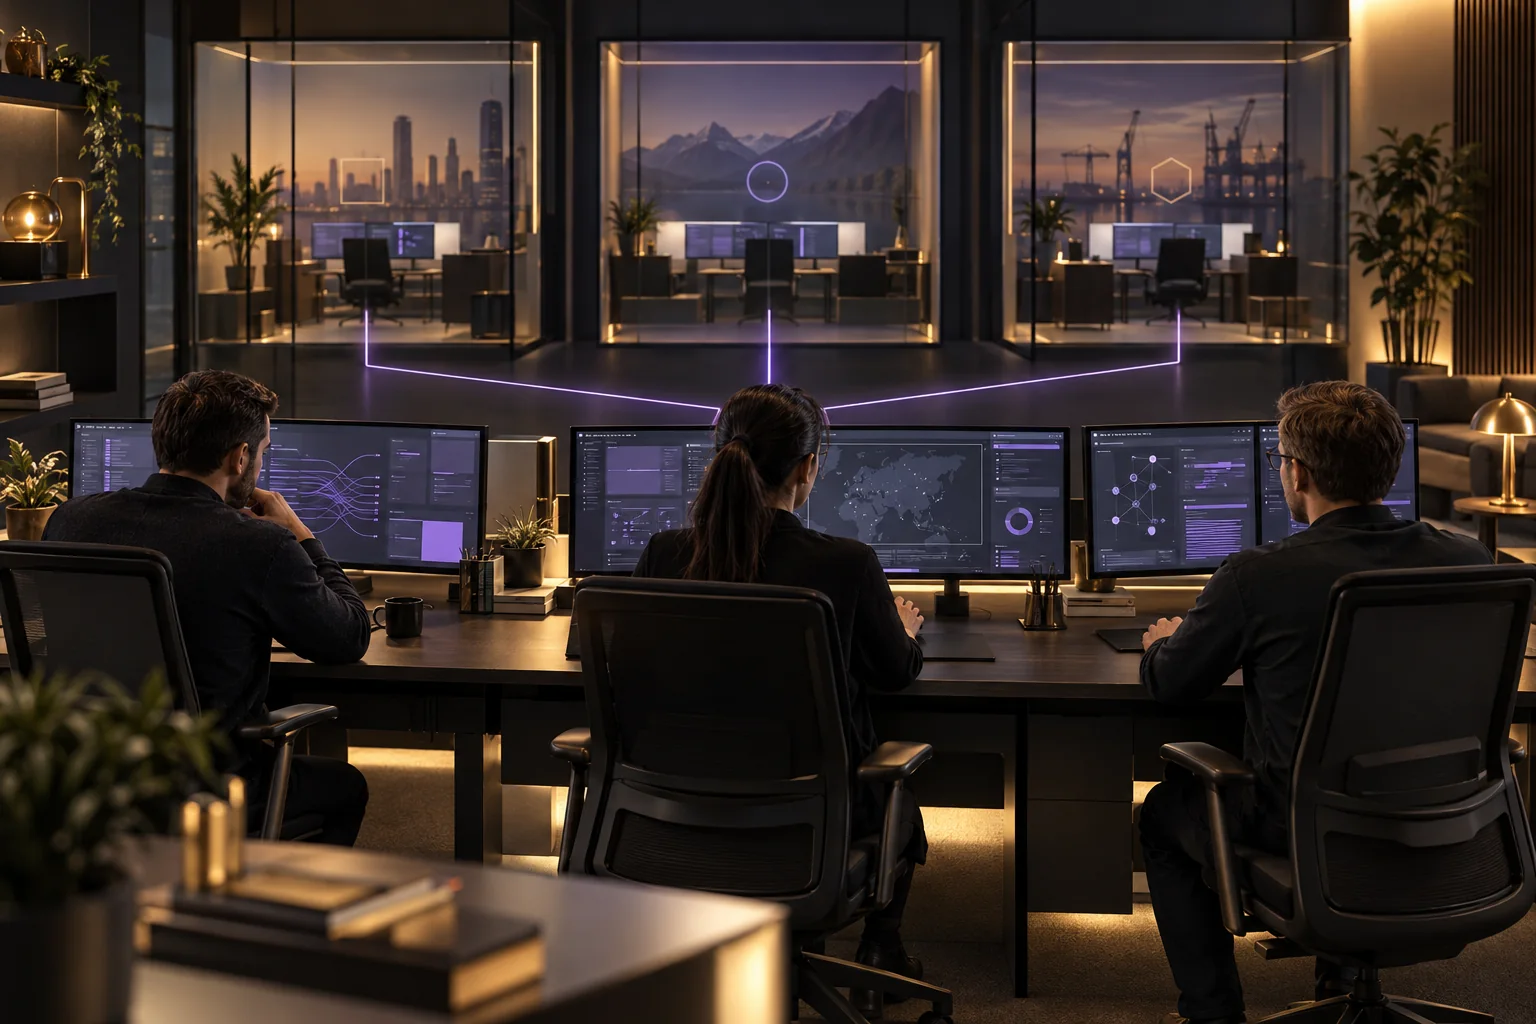
Xcitium offers SOC operations as a fully managed or co-managed service. Partners can bring the service to customers under their own brand.
Analysts and incident response
Xcitium specialists investigate alerts, respond to incidents, and help tailor response plans to each customer environment.
SOC and SIEM capabilities
Alongside SOC operations, a cloud-based SIEM service can be tailored to customer needs. Choose the level of management that fits the service model.
Threat detection across sources
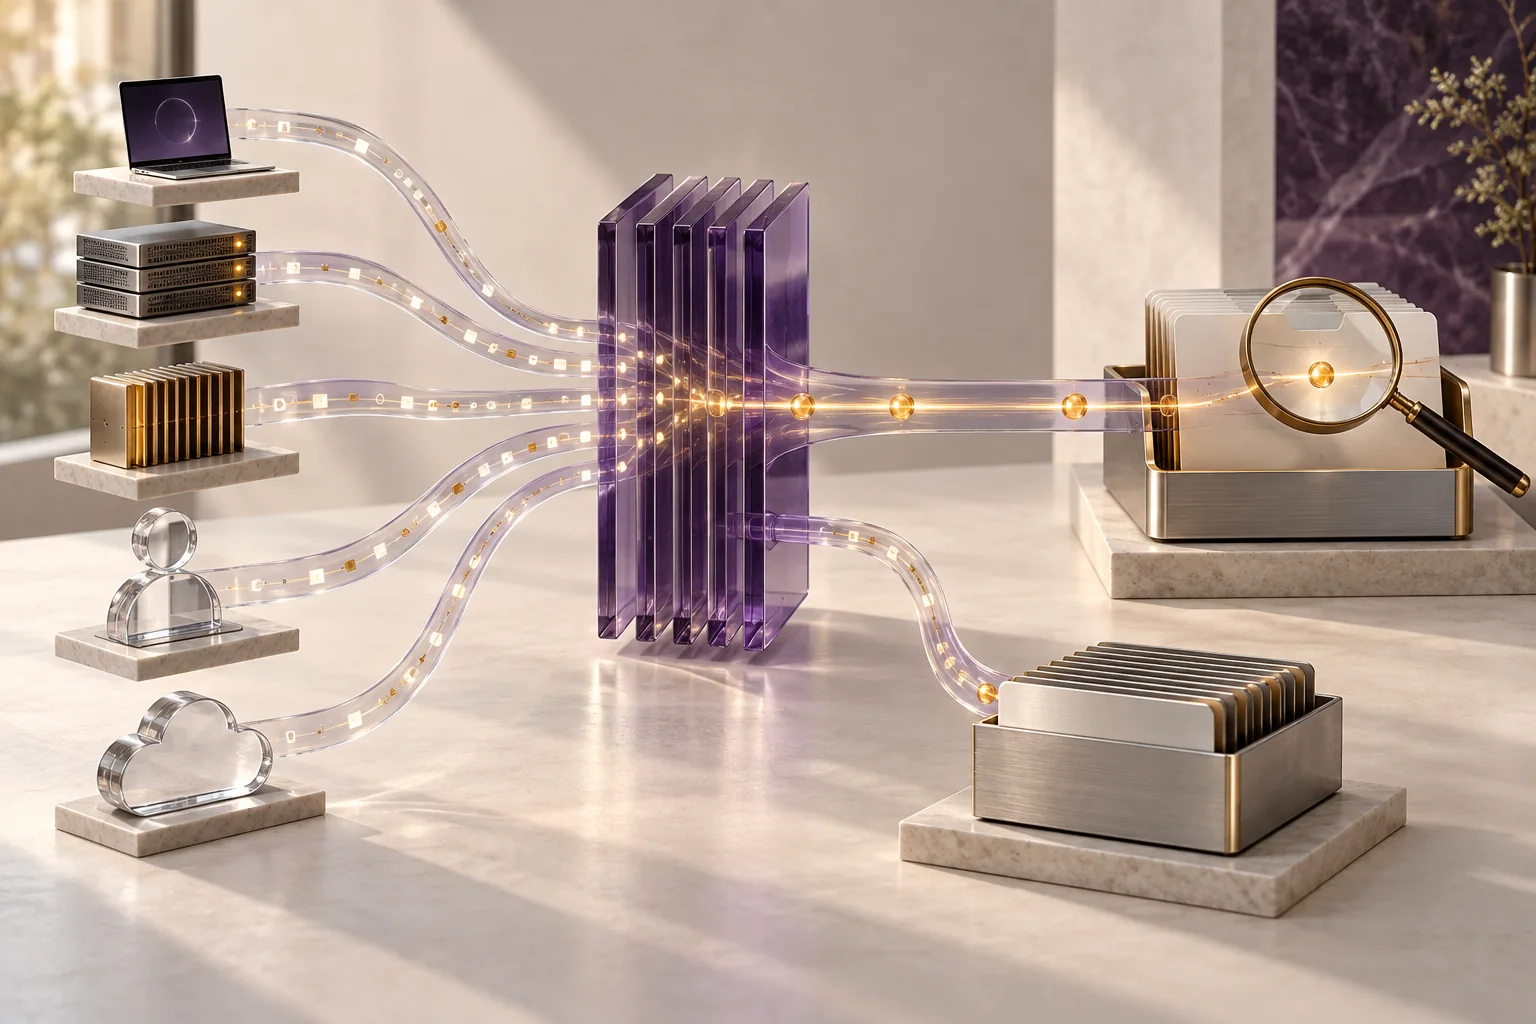
Logs, packets, network signals, and endpoint telemetry are correlated across physical, virtual, and cloud environments to give analysts investigation context.
Endpoint, intelligence, and asset onboarding
EPP/EDR and endpoint telemetry, intelligence from Threat Labs and Verdict Cloud, and automatic asset enrollment through a network scanner support the SOC workflow.
Xcitium
How it works
01Enroll assets+
Bring customer assets into the service through scanning and automatic enrollment.
02Collect telemetry+
Logs, network signals, and endpoint telemetry feed monitoring and correlation.
03Investigate events+
SOC analysts investigate threat signals and align response actions with the customer service model.
04Review outcomes+
Reports and response records help plan the next security steps.
Find the right solution

Questions and answers
What can the SOC service include?
The service model can combine SOC monitoring, SIEM, cross-source threat investigation, endpoint capabilities, and threat intelligence.
Is the service fully managed?
Xcitium describes both managed and co-managed options. The parties agree on how day-to-day responsibilities are divided.
Xcitium
A plan for your environment
Share your environment, current tools and priorities. Define the scope of the solution and the stages of deployment.