
Xcitium services
Managed threat services
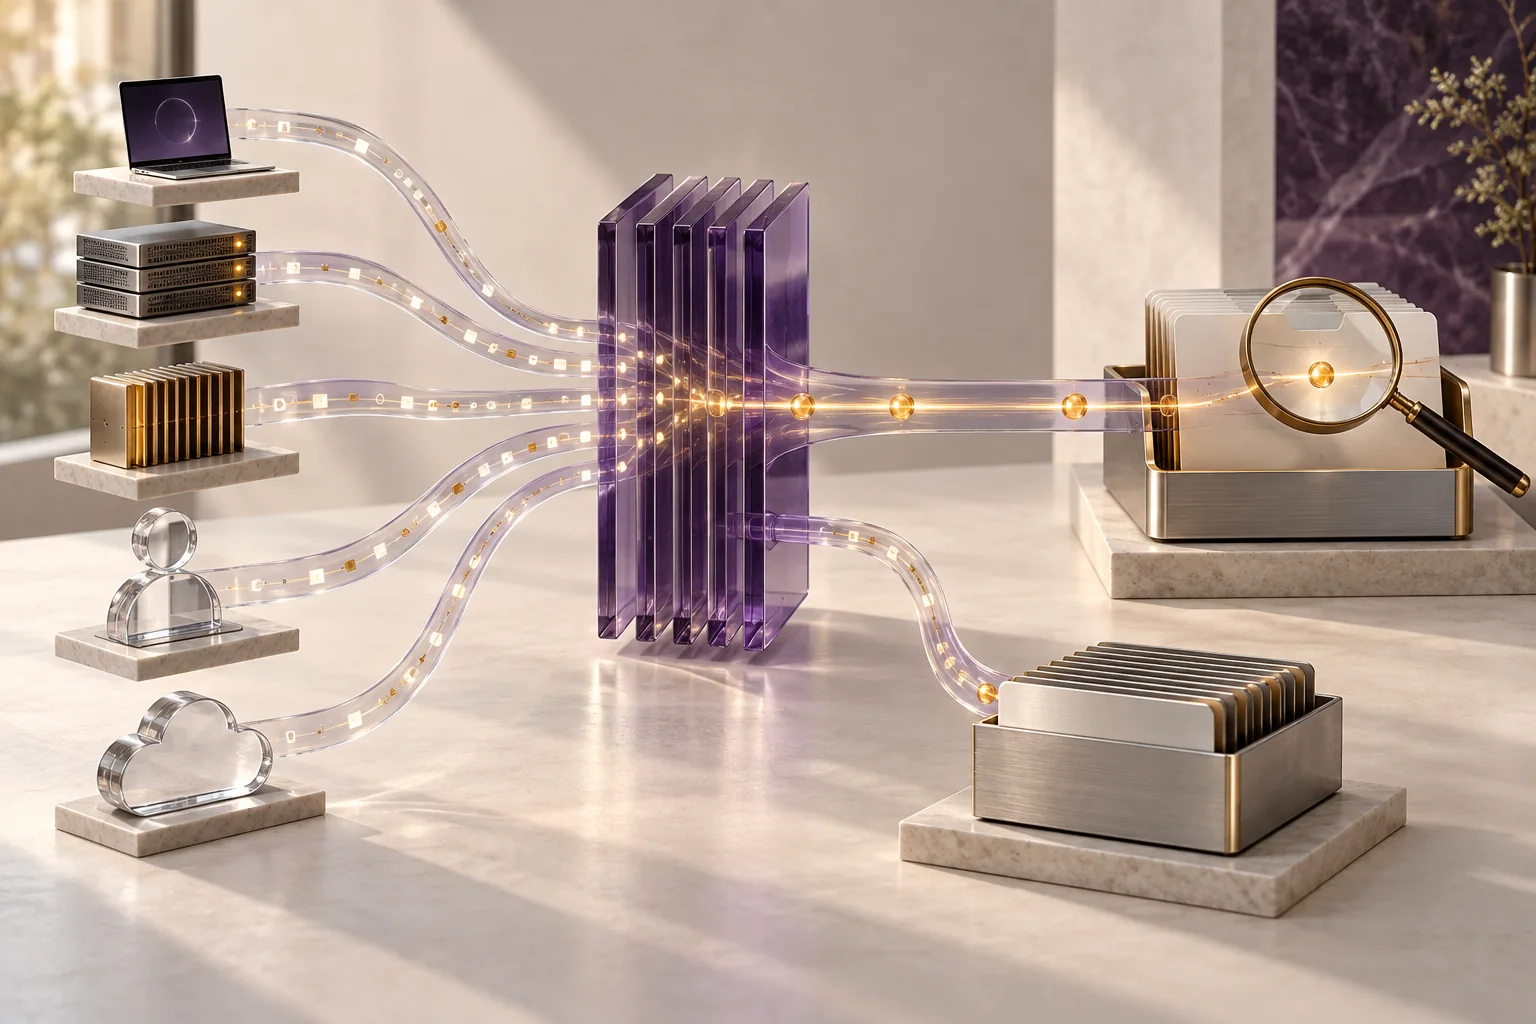
Continuous monitoring across network, endpoint, and cloud environments, with analyst investigation and response.
Discuss your requirements↗
Continuous monitoring
Xcitium describes 24/7 monitoring across network, endpoint, and cloud environments to watch for suspicious activity.
Automated detection and behavioral analysis
Machine learning and behavioral analytics help identify anomalies and potential threats; signals proceed to analyst review.
Expert investigation
Threat analysts investigate alerts to establish their nature and severity, helping reduce operational impact from false positives.
Containment and response
After a threat is confirmed, the MDR team can take containment and mitigation actions, isolate affected systems, and support restoration.
Proactive hunting and reporting
Analysts look for activity that may have evaded automated defenses. Reports summarize findings, response actions, and recommendations to strengthen defenses.
Evaluate a sample investigation
Choose the environment, signals and responsible owner. Use a sample investigated event to review evidence, mitigation authority and the resulting report.
Xcitium
How it works
01Monitor activity+
Network, endpoint, and cloud signals are monitored for ongoing analysis.
02Investigate suspicious activity+
Automated analytics identify anomalies; experts validate alerts and investigate their context.
03Take response actions+
Confirmed threats receive containment and other agreed mitigation actions.
04Review reports and recommendations+
Findings and response actions are presented with recommendations to strengthen defenses.
Find the right solution

Questions and answers
Which environments can be monitored?
Network, endpoint, and cloud environments can be included; exact coverage depends on the agreed service.
Is the service limited to automated detection?
No. It also includes analyst investigation, response actions, threat hunting, and reporting.
Xcitium
A plan for your environment
Share your environment, current tools and priorities. Define the scope of the solution and the stages of deployment.